If you think the world of digital security calms down as soon as Apple releases a security patch, you have yet to learn about the persistence of attackers. The malicious spyware DarkSword, which previously occupied security researchers, has not only remained active but has evolved, appearing in a new and more aggressive form. This newly discovered variant carries dangerous features that target your sensitive data and financial wallets, putting the security of unpatched iPhones to the test once again.
What is the DarkSword tool and why does it pose an exceptional risk?
The real danger of the DarkSword malware lies in the fact that it did not require technical genius to compromise victims; rather, it was a ready-to-use hacking kit. The tool consists of a collection of HTML and JavaScript files capable of infecting a target as soon as they are uploaded to any modest web server, without the need for deep programming expertise on the part of the attacker, which allowed even inexperienced individuals to launch complex attacks.
For example, in recent days, a malicious phishing page was spotted claiming to open pre-orders for a fake device called the “iPhone Duo” for $500. Simply opening that page via the Safari browser on unprotected iPhones or iPads was enough to download and install the malware immediately without any further user interaction.
According to reports from Google’s Threat Analysis Group, the DarkSword package was initially used by commercial spyware companies and state-sponsored actors to target iPhone users in several countries, including Saudi Arabia, Malaysia, Turkey, and Ukraine.
The new P7 variant: Human touches and theft of digital wallets
The new development in the landscape is what researchers at the security firm iVerify revealed, as they spotted an upgraded version of this tool they dubbed “P7 DarkSword,” a name inspired by the p7_ prefix adopted by the attacker in naming variables within the modified code. This variant was first discovered during a security scan of an infected device in August.
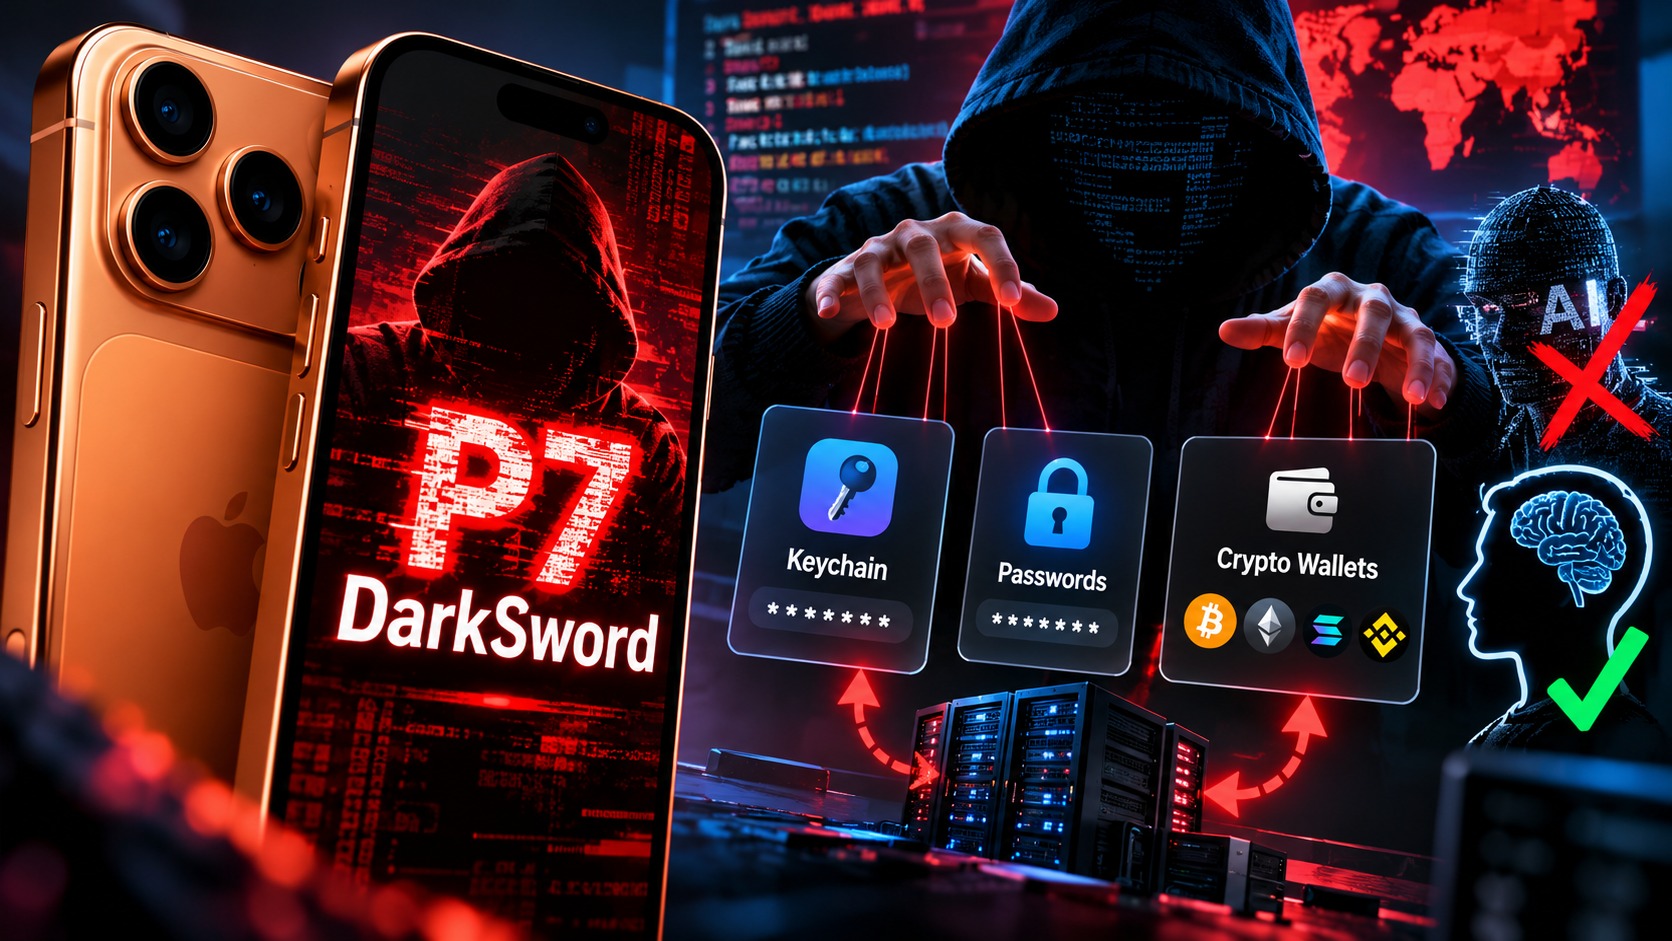
The P7 variant features several fundamental upgrades that make it more dangerous; it reduces its footprint and digital signature on the system to avoid detection, and it adds malicious capabilities to steal keys and passwords stored in the Keychain, in addition to targeting cryptocurrency wallets. Furthermore, the variant integrates a two-way communication system with the hackers’ command-and-control servers.
The most interesting thing is that researchers noted that most previous variants were the result of random software generation via artificial intelligence, while the P7 variant bears clear human fingerprints; its developers invested real effort and showed high programming efficiency in restructuring the tool to make it more stable, stealthy, and effective.
Are iPhones safe from this Dark Sword?
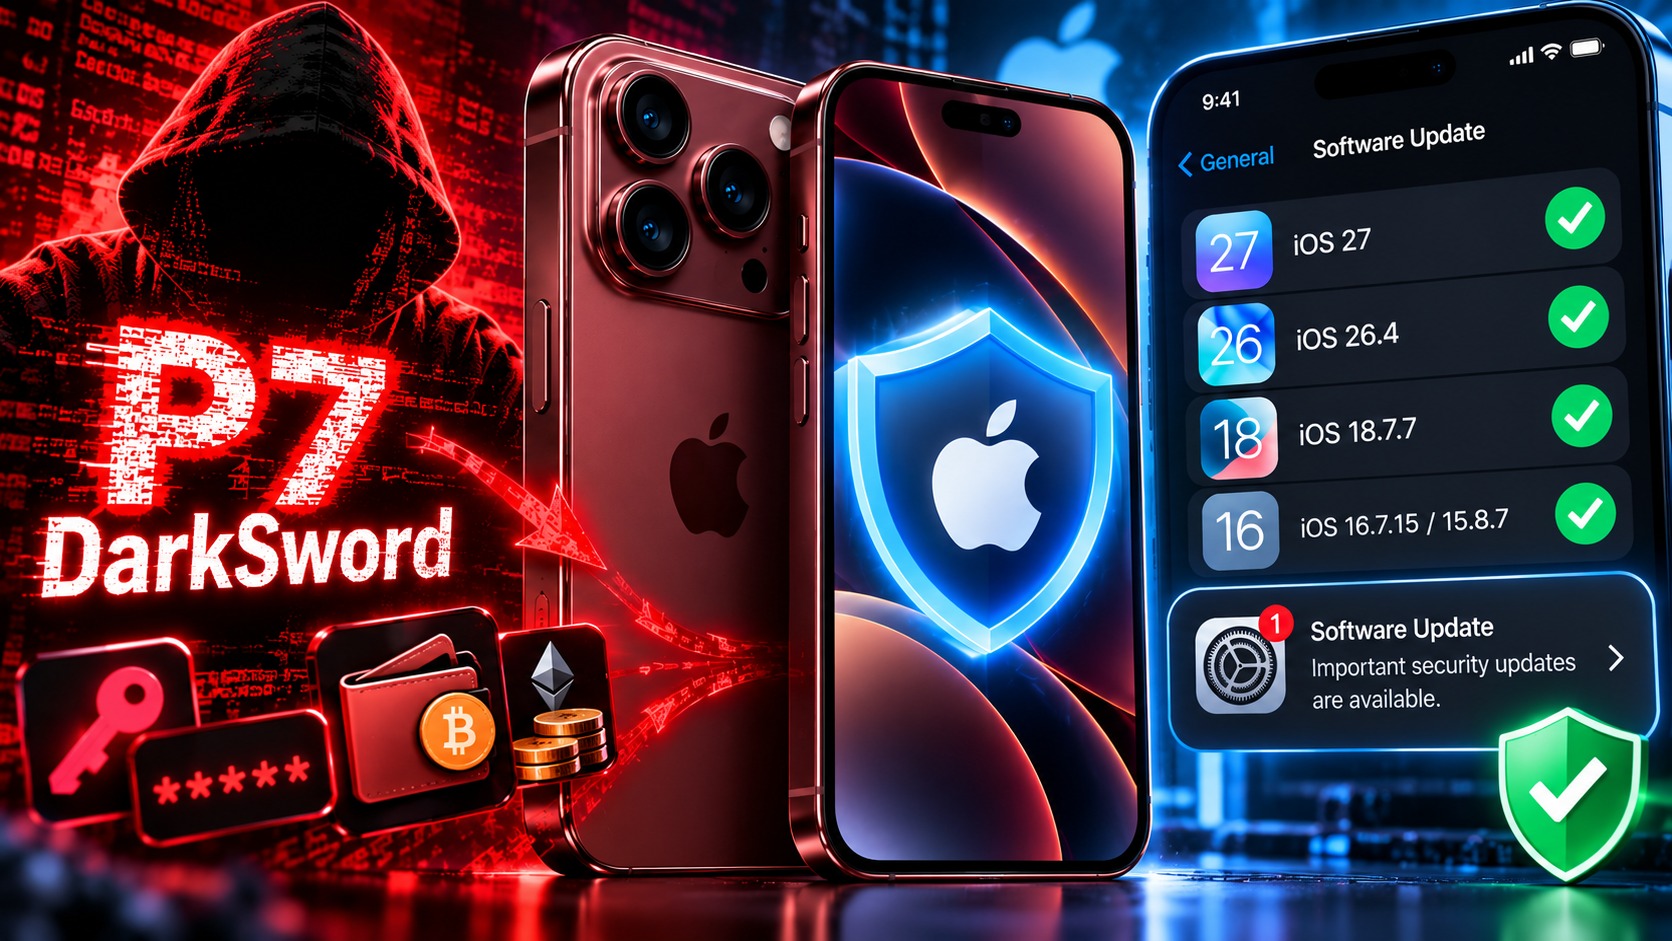
The reassuring news amidst these alarming details is that Apple’s defense arsenal is still holding up successfully. Security indicators and reports confirm that there is no evidence proving the P7 variant’s ability to compromise devices that have already received the security updates released by Apple to address the original DarkSword vulnerabilities in iOS 18.7.7, iOS 26.4, iOS 27, and later versions, in addition to updates for older devices such as iOS 16.7.15 and iOS 15.8.7.
The real danger is entirely limited to devices that have fallen behind on updates and are running old, unpatched versions. Always remember that ignoring the small red notification in Settings is not a sign of caution, but is often an open invitation for such malicious tools to settle inside your device and steal the most valuable personal and financial data you own.
Source:
Leave a Reply