In a remarkable security development that brings back memories of the golden age of the jailbreak community, cybersecurity firm Calif has demonstrated a unique technical achievement: running an untethered jailbreak on an iPhone 18 Pro running iOS 27.0.1. The significance of this demonstration lies not only in bypassing Apple’s latest security barriers but in the modified system’s ability to persist even after a full device reboot—a feature that has been extremely rare in the modern security landscape after years of dominance by semi-tethered tools.
Hexacon Conference and Full Root Privileges
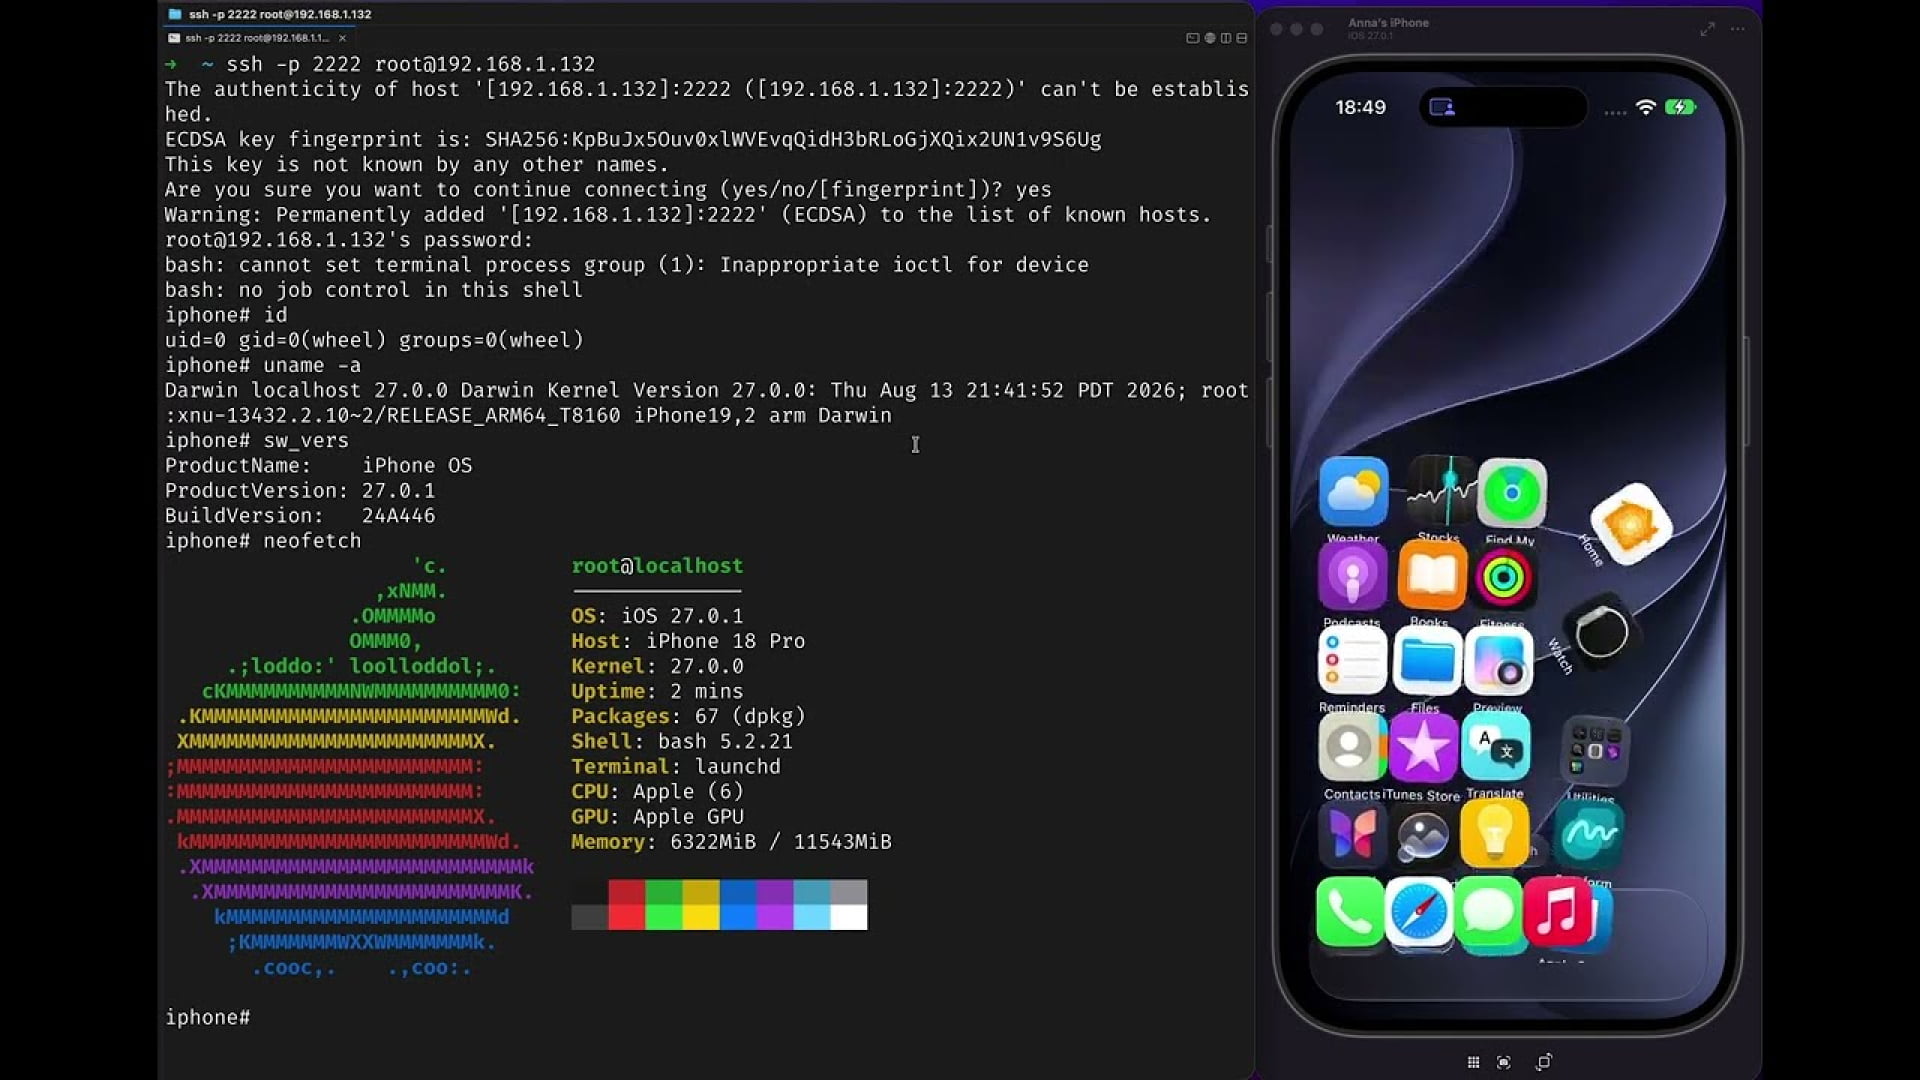
The security team revealed this achievement during the Hexacon cybersecurity conference held in Paris, France, and published video recordings documenting the jailbreak details. The first clip showed an SSH connection to the phone with full root privileges, where the terminal displayed the uid=0 identifier, confirming the attainment of the highest level of control within the system.
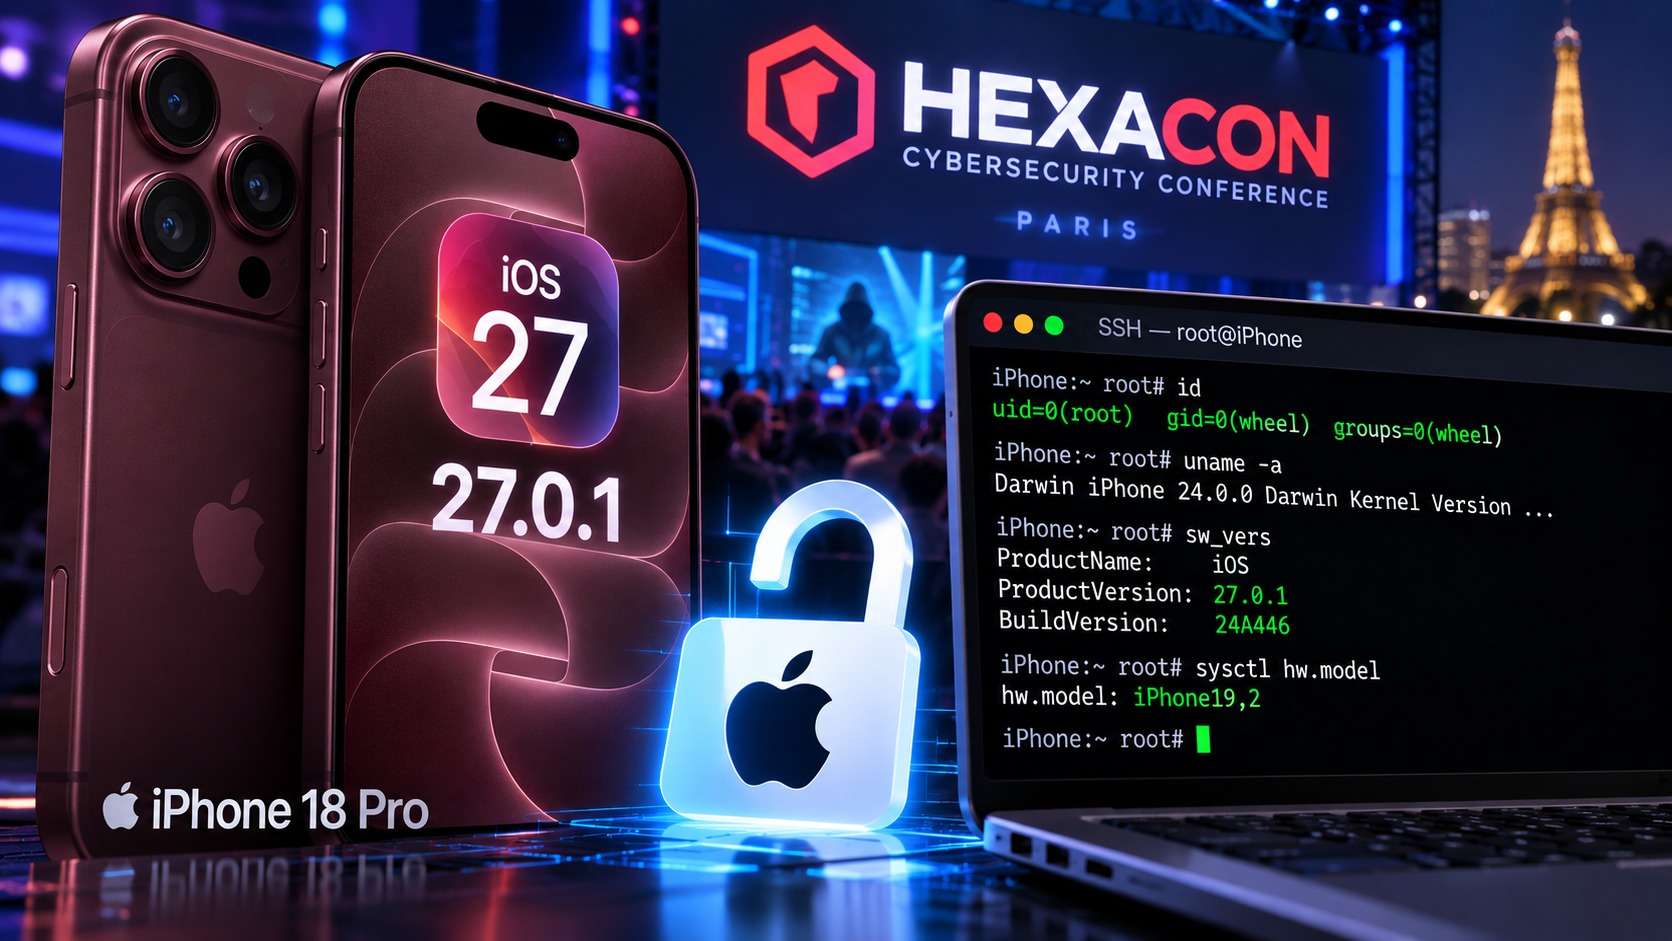
Terminal data clearly showed that the hardware carries the identifier iPhone19,2 and runs iOS 27.0.1, build number 24A446, which is the latest update officially released by Apple. These deep privileges grant the software session access that no standard App Store application could achieve, bypassing all of Apple’s strict sandbox restrictions.
Untethered Jailbreak Survives Reboot
The most impressive feature is the persistence of the software modification. In another video titled “iPhone 18 Pro Persistent Jailbreak,” researchers demonstrated restarting the phone and then unlocking it using the user’s standard passcode, with the system returning directly to its modified state without losing the jailbreak. This specifically means it is an untethered jailbreak that does not require re-activation via a computer or app after every shutdown.
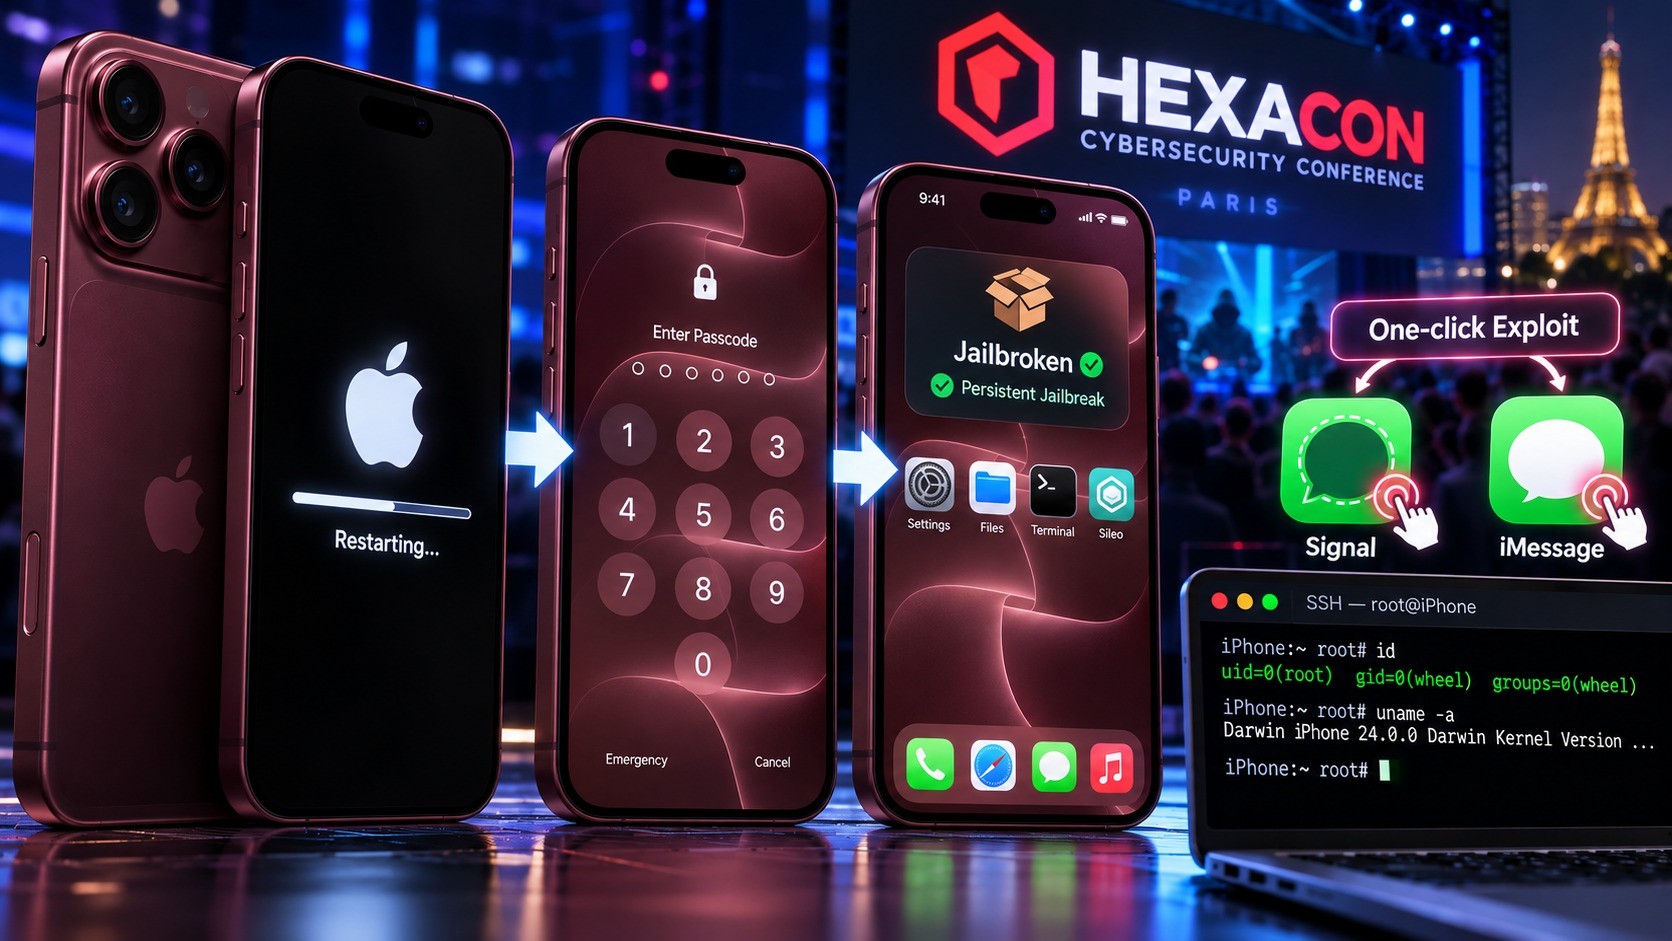
It should be clarified that this experiment is not intended to bypass the device owner’s lock screen passcode, but focuses exclusively on the stability and persistence of the exploits across power cycles. The post also included a demonstration of one-click exploits targeting communication apps like Signal and iMessage, without delving into the details of the root vulnerabilities underlying the breach.
Will we see a public jailbreak tool soon?
Despite the excitement this demonstration has sparked among users, it did not include the release of any public tool or a release date. The team simply stated that everything will be disclosed in due time, without clarifying whether this means releasing a tool ready for the end-user or publishing security research and code intended only for developers and researchers.

The company also did not reveal a list of other devices or versions supported by these vulnerabilities, while Apple’s official security page still lists iOS 27.0.1 as the latest stable version available to the public, meaning Apple will begin its investigation to close these loopholes in future security updates.
Comparison with current jailbreak tools
The current state of public jailbreak tools remains highly restricted to specific devices and versions. For example, the Dopamine 3.0 tool supports iOS 26.0 through 26.0.1 only and is limited to devices equipped with A12 and A13 processors, in addition to being a semi-tethered tool that requires re-running the app and activating it with every reboot.
Source:
Leave a Reply