Apple has released a new minor operating system update, version iOS 27.2.1, aimed at users who have not yet moved to the iOS 27.3 beta versions. As is typical with quick minor updates, you may not find visually stunning features or entirely new interfaces here; however, its true importance lies in the solid security wall it builds and the patching of vulnerabilities that could threaten your privacy, specifically the strange and embarrassing bug that affected the iMessage chat app.
iMessage group vulnerability: Privacy in jeopardy
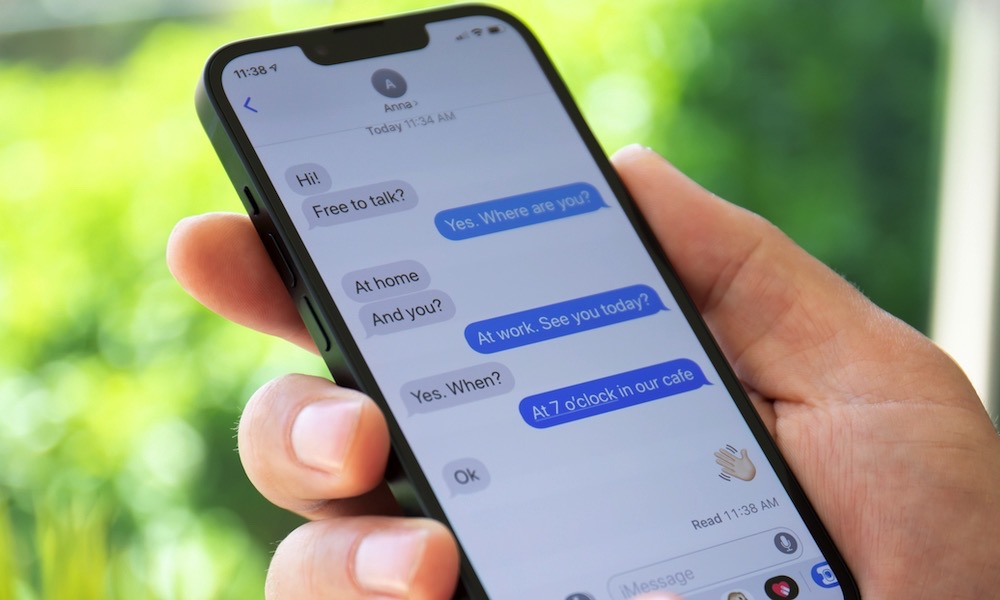
The main feature that has always set iMessage apart from platforms like Messenger and WhatsApp is its strict respect for old chat history; when you add a new member to a group chat, they are not supposed to be able to see messages exchanged before they joined. However, Apple admitted to an unintentional flaw that allowed a newly added user to access previous messages sent before they joined—a dangerous scenario that could expose sensitive information, whether it be work secrets or a family surprise you didn’t want revealed.
The most sensitive aspect of this vulnerability is the lack of any way to know if the new member has actually managed to read the previous messages, unless they disclose it themselves. Security notes also pointed to a related vulnerability that could allow a remote attacker to join an iMessage group chat and receive its messages, prompting Apple to act quickly and fundamentally remove the code causing the issue.
Bluetooth and AirPlay vulnerabilities
The update was not limited to iMessage; it also included an important patch for a set of vulnerabilities related to Bluetooth connectivity and the AirPlay service. The vulnerability allowed an attacker within close Bluetooth range to corrupt memory or even pair with the device without any user interaction. This dangerous exploit could have allowed a hacker to monitor audio being played on your device and potentially control some device functions remotely.
Apple clarifies that these security vulnerabilities have not been actively exploited so far. However, once the company publishes the list of fixes and technical details publicly, hackers begin looking for devices that have not yet updated to exploit those open doors. Therefore, updating promptly is the first and most essential preventive step for every user.
Synchronized updates across the Apple ecosystem
Because Apple’s security ecosystem works as a single unit, the company simultaneously released a wide package of updates for all its other devices to address the same issues:
- Tablet updates: iPadOS 27.2.1, iPadOS 26.7.3, and iPadOS 18.7.12.
- Watch updates: watchOS 27.2.1 and watchOS 26.6.1.
- Smart glasses updates: visionOS 27.2.1.
- Mac updates: macOS Golden Gate 27.2.1, macOS Tahoe 26.7.3, and macOS Sequoia 15.8.3.
It is also noted that the iOS 18.7.12 update was released, which addressed only the Bluetooth and AirPlay issues without mentioning the iMessage vulnerability, confirming that the chat history bug was a software error that recently crept into newer versions. We advise everyone to open Settings, go to General, and then Software Update to install these improvements immediately to keep their data and privacy secure.
Source:
Post Comment